2F Game Warden
Fully Accredited DevSecOps Platform
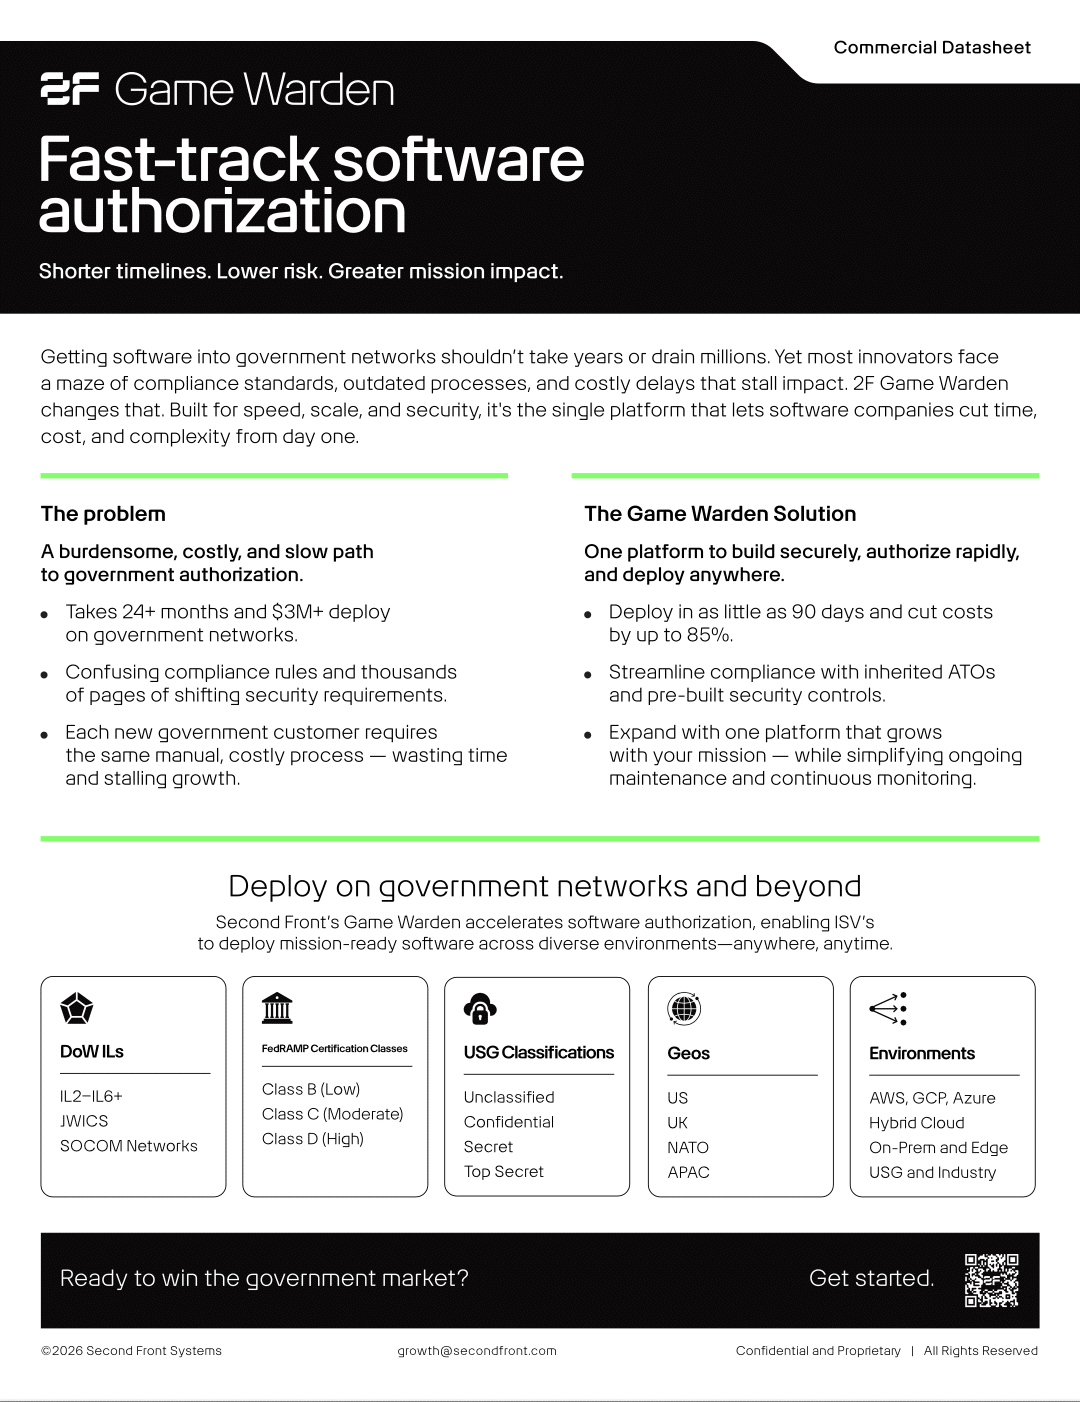
2F Game Warden helps commercial innovators deliver technology that fills agency capability gaps and helps government teams launch or modernize mission applications. Both reach accreditation in as little as 90 days and cut costs by up to 85%.
IL2 - IL6+ | FedRAMP | GovRAMP | Allied
Inherit established security controls to compress the ATO process from years to months and deploy to civilian agencies, defense networks, state and local services, and disconnected environments.
Treat compliance as ongoing operations, not a one-time milestone, using automated workflows and built-in security to reduce recurring work as regulations evolve.
Second Front’s SOC ingests application telemetry to deliver continuous monitoring, automated threat mitigation, and rapid platform-, network-, and application-level incident response to protect your software and preserve its accreditation.
Generative AI agents automate CVE research and vulnerability remediation, simulation environments validate mission readiness, and LLM-as-a-Service and self-hosted models stay within secure boundaries.
Leading software providers and government agencies worldwide trust Second Front.
Bring your application. We supply the rest of the stack, all the way down to the disconnected edge.
Applications & Experience
Where your applications run. Deploy and update across every environment you serve, and give your end users secure access to the mission software they rely on.
Security & Compliance
Continuous scanning of containers, and configurations produces the live evidence authorizing officials need to grant and keep an ATO.
Control Plane
Each landing zone sets the security requirements, compliance frameworks, networking, and identity for its environment. Every workload deployed there inherits them.
Secure Connectivity
Agents connect outbound only, so no environment ever opens an inbound port. That means a smaller attack surface and a simpler path through network approvals.
Game Warden Runtime
Containerized and non-containerized workloads run under the same policy, security, and observability, with controls your ATO inherits instead of rebuilding.
Cloud & Virtual Infrastructure
Run across commercial and government clouds and virtual machines, provisioned the same way everywhere.
Physical & Edge
Bare metal, disconnected sites, air-gapped networks, and embedded devices, all provisioned and managed like any other environment.
DOW
AUTHORIZATION
2F Game Warden for DOW automates and simplifies the Authorization to Operate (ATO) process, so programs can field mission-critical capabilities on a predictable timeline and plan their workforce around it. Applications have been successfully deployed across IL2 through IL6, including NIPR, SIPR, and JWICS, and Game Warden holds multi-service specific ATOs.
FEDRAMP CERTIFICATION
2F Game Warden for FedRAMP® offers three flexible pathways scoped to mission requirements: the 2F boundary, your own boundary, or equivalency. Game Warden delivers monitoring data, vulnerability trends, and scan history in machine-readable formats such as OSCAL, supporting VDR and VER reporting for the 20x model.
UNIFIED SECURITY
2F Game Warden protects sensitive data for DOW, federal civilian, state, local, education, and tribal organizations through application scanning, penetration testing, and more.
For DOW: DoD DevSecOps Reference Design and a zero Critical or High CVE posture.
For FedRAMP: 416 controls documented in the System Security Plan and support for the 20x model.
For GovRAMP: Tiered baselines from 60 controls at Core to 300+ at Authorized, with continuous monitoring and validation.
CLOUD COMPATIBILITY
Second Front maintains partnerships with AWS, Google Cloud Platform, and Microsoft Azure to support secure deployment across their environments, models, and services.
MODERN
CI/CD EXPERIENCE
2F Game Warden provides the infrastructure to run your software, from security and CI/CD pipelines to database management and Day 2 logging, monitoring, and alerting. Spot performance and security risks in real time with built-in observability.
PROACTIVE SUPPORT
2F manages and optimizes your deployed software for Day 2 operations, reducing demands on your engineering and security teams while maintaining stability, scalability, and performance. Around-the-clock monitoring across platform, network, and application logs keeps your current security posture visible to agency customers, with rapid containment support and reporting aligned to incident response SLAs. Second Front streamlines feature requests, offers strategic consultations, and holds regular check-ins as you grow.
EXPANSION READINESS
2F Game Warden includes the body of evidence that supports current and additional deployments to secure government networks, making it easier to expand into new departments, agencies, and regions.
2F Game Warden holds a FedRAMP Class D (High) Certification and a GovRAMP High Authorization, and supports the full DOW Impact Level spectrum (IL2-IL6) across NIPR, SIPR, and JWICS deployments. Second Front customers inherit up to 80% of controls, with application-layer security (your code, access model, and data handling) as the only customer responsibility. Explore FedRAMP Certification and DOW Authorization.
Not on its own. 2F Game Warden accredits software and deploys it to secure government networks, including disconnected environments. To run authorized software on edge hardware, 2F Frontier delivers it to the device and keeps it running when the connection drops. See how 2F Frontier takes authorized software to the edge.
Yes. Government teams can launch or modernize mission applications on 2F Game Warden, using the same accredited platform and inherited security controls as commercial software providers.
20x defines what a modern path to FedRAMP Certification looks like, but it does not do the work behind the submission. 2F Game Warden for FedRAMP® helps providers scope a right-sized boundary to the systems that touch federal data, see how their offering runs day to day, and keep structured evidence current as changes ship, so each agency can match security goals to its own mission. Get 20x in plain English.
Second Front manages the infrastructure, the platform, and continuous monitoring. Customers own their application code, container builds, and vulnerability remediation, and share security testing with Second Front. Review the shared responsibility model.
Yes, whether you run on a provider today or are considering a move. Second Front maintains partnerships with AWS, Google Cloud Platform, and Microsoft Azure to support secure deployment across their environments, models, and services, so you can build on the provider you prefer. Discover 2F Managed Services.
Dummies eBook
Government authorization doesn’t have to be a black box. Learn how it actually works.
Partners
Partnerships with mission-owners, cloud providers, incubators, and value-added resellers enhance our offerings while furthering our mission to deliver emerging technologies to the world’s democracies.
Learn more
We’re ready to help you deliver your software to all levels of government.
Find out how we can help you accelerate accreditation.